What’s new with Echo
Stay up-to-date on Echo’s latest feature drops, platform improvements, and product updates.
Pull vetted and patched NuGet packages from Echo
September 2026
The full public NuGet ecosystem is now available through Echo – malware-screened, source-validated, and patched for critical and high CVEs on the versions you already use. Pull packages through the dotnet or NuGet CLI, JFrog, or Nexus without upgrading your framework.
Get notified when Echo acts on your behalf
September 2026
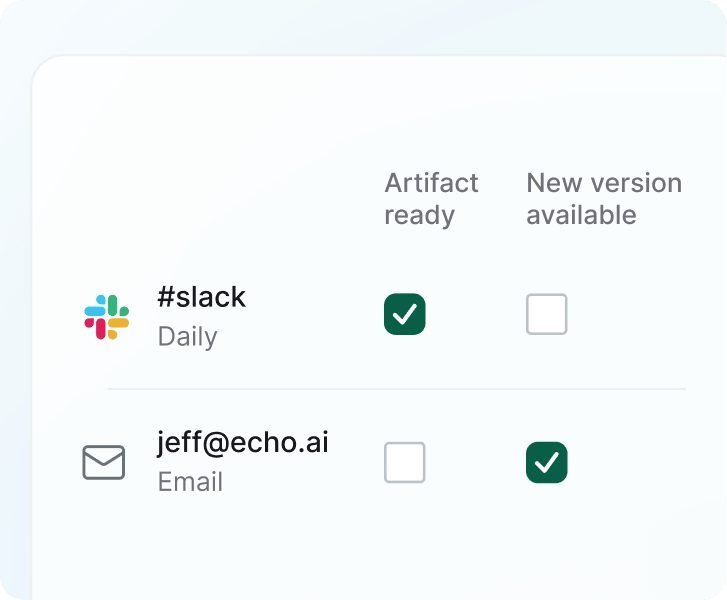
Automatically stay updated on the Echo events that matter to your environment – whether a requested artifact goes live, a new version of something you’re already using is published, or a high-profile CVE gets patched.
See exactly what you're pulling from Echo
September 2026
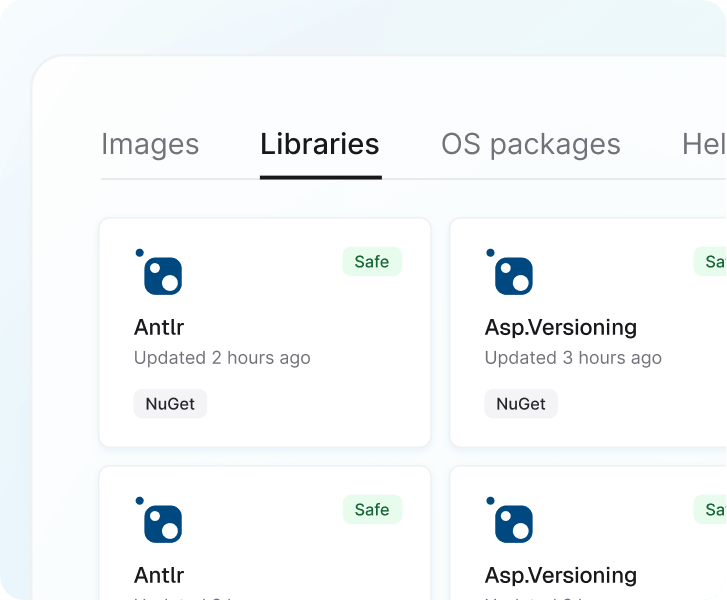
Get a complete view of every artifact your team pulls from Echo – across container images, libraries, Helm Charts, etc. See which versions you’re using, when they were last pulled, and how often, then filter, search, or export your inventory to find the info you need.
Echo now fits your JFrog Curation policy
September 2026
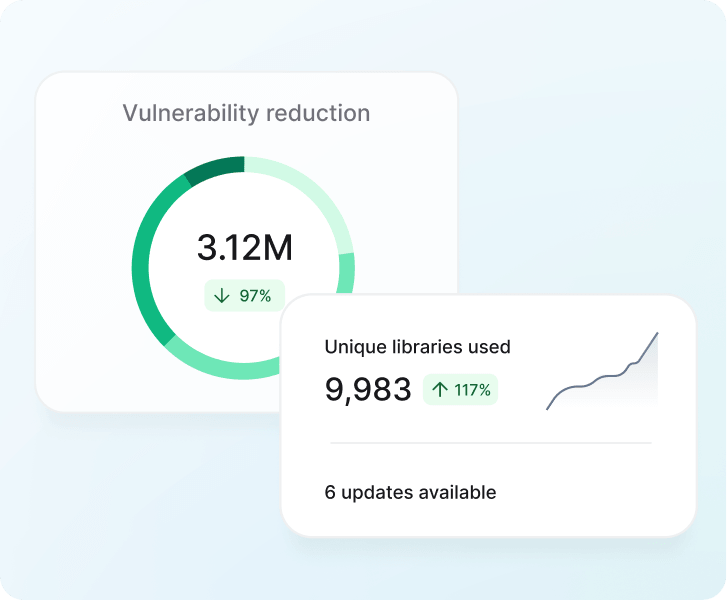
Echo repositories are now recognized as a vendor source in JFrog Curation across every ecosystem, so you can adopt Echo without creating exceptions to the policies you already use to govern licenses, vulnerability levels, and upstream content.
Echo VMs are officially in beta
August 2026
Echo now has a hardened, CVE-free operating system you can run as an AMI, VM or install on bare metal. Same drop-in experience as Echo containers, now across the whole machine. It's STIG-hardened, FIPS-validated, and ships with an audit-ready evidence package.
Every PyPI, npm, and Maven package is now searchable
August 2026
Search any package in Echo and instantly see its status – Safe, Safe & Patched, or Available. The catalog refreshes daily and includes the install command for every package.
Echo container images now scan clean with Snyk
August 2026
Snyk now accurately reflects Echo’s vulnerability-free images – without false positives for fixed CVEs or findings that need to be manually suppressed. The result is cleaner scans and a secure foundation.
Echo libraries have expanded
July 2026
Echo's Maven and npm library ecosystems are now fully available, alongside PyPi. Every package in both indexes is pre-vetted for supply chain safety, with patched versions for critical and high CVEs.
Libraries scan clean with Trivy and Grype
July 2026
Patched npm packages pulled from Echo now scan clean in Trivy and Grype. Load Echo's VEX file into your scanner to watch patched CVEs disappear from your results.
Mirror Echo Libraries to your artifactories
July 2026
Echo now supports mirroring Echo Libraries directly to your own private JFrog, GAR, and Nexus Artifactories. A single remote repository per ecosystem, without the need for fallbacks or complex setup.
Echo libraries now in beta
May 2026
We’ve officially launched our beta for our secure Python libraries that are built to prevent supply chain attacks across dependencies without breaking builds.
New Echo helm charts are now available
May 2026
Drop in our helm charts that replace both Bitnami and upstream alternatives, and smoothly deploy Echo’s regular and FIPS-validated images.
Additional integrations just dropped
May 2026
Echo now supports Harness, Amazon Inspector (AWS ECR), Palo Alto, and has extended its Wiz integration to also support libraries.